Two-Factor Authentication vs Two-Step Verification: What’s the Difference?
When you sign in to an online account, entering your password may not be enough. Many websites and applications ask you to complete another verification step before allowing access. You might receive a code on your phone, approve a notification, or use a fingerprint to confirm your identity.
These additional checks are commonly associated with two-factor authentication (2FA) and two-step verification. Although the terms are often used interchangeably, they don’t necessarily describe the same thing.
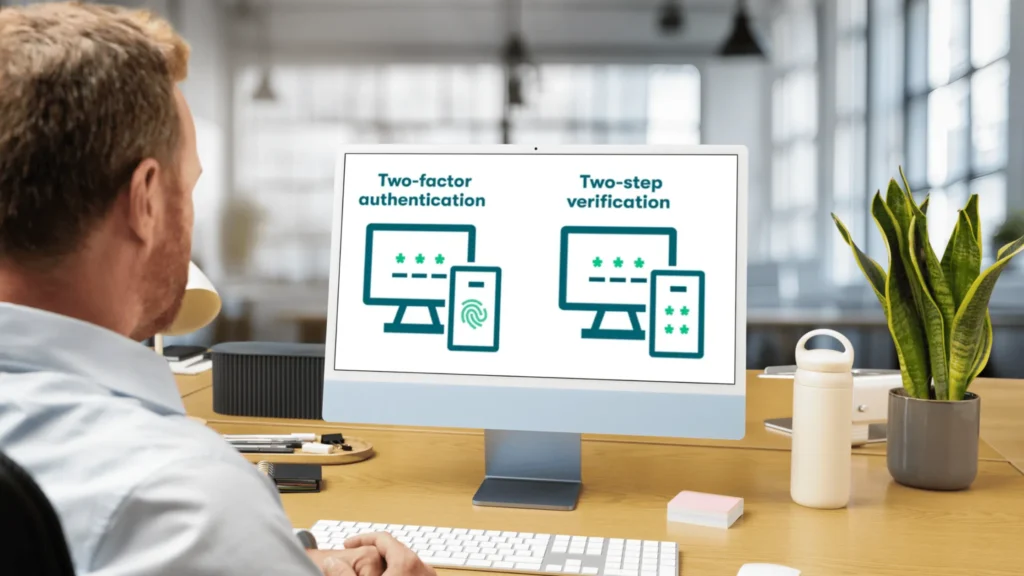
The difference comes down to how an authentication system verifies your identity. Two-factor authentication requires two different types of authentication factors, while two-step verification describes a login process involving two verification steps. Those steps don’t necessarily have to use different factors.
Understanding this distinction makes it easier to evaluate the security of your accounts rather than assuming that every additional login screen provides the same level of protection.
What Is Two-Factor Authentication (2FA)?
Two-factor authentication is a security method that requires two different authentication factors to verify a person’s identity before granting access to an account or system.
Instead of relying entirely on a password, it combines different categories of evidence. This means that someone who obtains your password still needs to satisfy the second authentication requirement.
Authentication factors generally fall into three categories:
- Something you know: A password, PIN, or other secret information.
- Something you have: A registered security key, trusted device, or suitable authentication token.
- Something you are: A biometric characteristic, such as a fingerprint or facial recognition.
For example, imagine signing in to your email account using a password and then confirming your identity with a registered hardware security key. Your password represents something you know, while the security key represents something you have.
Because these belong to two different authentication categories, this is an example of two-factor authentication.
The important point is that having two credentials doesn’t automatically mean an account uses two-factor authentication. A password followed by another PIN still relies on something you know.
How Does Two-Factor Authentication Work?
A typical two-factor login process involves the following stages:
- You enter your account username and password.
- The service checks your login credentials.
- It requests another authentication factor.
- You provide the required verification.
- The service checks the second factor and grants access if everything is valid.
The exact process depends on the technology used by the service. Some systems require a separate verification action, while certain multi-factor authenticators can combine multiple factors within one authentication event.
The purpose remains the same: make unauthorized access more difficult by requiring independent evidence of identity.
What Is Two-Step Verification?
Two-step verification is a security process that requires users to complete two verification steps before accessing an account.
The first step is usually entering a password. The second might involve receiving a code, approving a notification, or completing another identity check.
For example, imagine logging in to a website with your password and then entering a six-digit code sent to your phone. You have completed two separate verification steps.
However, the number of steps doesn’t automatically tell you how many different authentication factors are involved.
Consider a system that asks you to enter a password and then enter a separate PIN. Both credentials belong to the knowledge category. Although the process involves two steps, it doesn’t qualify as two-factor authentication under the traditional definition.
This distinction explains why two-step verification and two-factor authentication can overlap without always meaning exactly the same thing.
How Does Two-Step Verification Work?
A typical two-step verification process looks like this:
- Open the website or application you want to access.
- Enter your username and password.
- Complete the additional verification request.
- Wait for the service to validate the information.
- Access your account once verification succeeds.
The second step varies between platforms. Some services send a one-time password through SMS, while others use authentication applications, email codes, or device notifications.
Google, for example, calls its account security feature 2-Step Verification and also describes it as two-factor authentication. This is a useful reminder that technology companies don’t always use these terms according to their strict technical definitions.
Two-Factor Authentication vs Two-Step Verification: Key Differences
The main difference between two-factor authentication and two-step verification is what each term describes.
Two-factor authentication focuses on the types of evidence used to establish identity. Two-step verification focuses on the sequence of verification actions required during login.
Here’s how they compare:
| Feature | Two-Factor Authentication | Two-Step Verification |
|---|---|---|
| Main purpose | Verify identity using two different factors | Require two verification steps |
| Main focus | Authentication factor categories | Verification process |
| Different factors required? | Yes | Not necessarily |
| Can use password and PIN? | Not as two distinct factors | Yes |
| Can involve a security key? | Yes | Yes |
| Security level | Depends on the methods and implementation | Depends on the methods and implementation |
| Relationship | A specific form of multi-factor authentication | A description of a two-step login process |
The table highlights an important distinction: neither the number of login screens nor the name of a security feature tells the whole story.
A two-step process can implement genuine two-factor authentication, but two steps alone don’t prove that it does.
Authentication Factors vs Authentication Steps
One of the easiest ways to understand the difference is to separate the evidence used during authentication from the actions performed during login.
An authentication factor represents a category of evidence. An authentication step represents an action in the verification process.
For instance, entering a password is one action that uses a knowledge factor. Confirming a login with a registered security key is another action that uses a possession factor.
Now consider a different situation. A website asks for a password and then a PIN. Although the user performs two actions, both depend on knowledge-based credentials.
This is why authentication steps and authentication factors shouldn’t be treated as interchangeable terms.
The distinction becomes especially important when evaluating account security. A service might advertise an additional verification step, but users should understand which authentication methods are actually being used.
Can Two-Factor Authentication Happen Without Two Separate Login Steps?
Yes. Two-factor authentication doesn’t always require two visibly separate actions.
Certain multi-factor cryptographic authenticators can combine multiple authentication factors into a single authentication event.
For example, a supported security system might use a cryptographic device together with local user verification, such as a PIN or biometric check. The user may experience this as one smooth sign-in action rather than two separate screens.
Passkeys are a useful example of this modern approach.
Depending on their implementation and the required user verification, passkeys can provide multi-factor authentication using a cryptographic credential protected by a device-level PIN or biometric check.
This is different from the traditional experience of entering a password and then manually typing a verification code.
The distinction is useful because it shows that strong authentication isn’t necessarily about adding more screens to the login process. The quality and independence of the authentication factors matter more.
Why Does Google Call It 2-Step Verification?
Google provides a practical example of why these terms can become confusing.
Its account security feature is officially called 2-Step Verification. However, Google also uses the term two-factor authentication when describing the additional protection.
When signing in, users may be asked to enter a password and complete another verification request. Depending on their account settings and available devices, this could involve a phone notification, authentication code, security key, or passkey.
The terminology reflects how the feature is presented to users rather than establishing a universal technical distinction between every possible authentication configuration.
For readers, the lesson is straightforward: don’t judge an account’s security simply by whether its settings say 2FA or 2-Step Verification.
Look at the actual authentication methods, how they work, and whether they protect against common attacks.
Which Is More Secure: Two-Factor Authentication or Two-Step Verification?
Neither term automatically guarantees stronger security.
Two-factor authentication requires different authentication factors, but the strength of the individual methods still matters. Similarly, two-step verification can provide meaningful protection when its steps use appropriately independent and secure authentication methods.
For example, a password combined with an SMS verification code provides additional protection compared with a password alone. However, SMS codes can be targeted through SIM swapping and phishing attacks.
On the other hand, a properly implemented FIDO2 security key can provide phishing-resistant authentication.
The difference isn’t simply about having two checks instead of one. It’s about how effectively the authentication system prevents an attacker from impersonating a legitimate user.
Several factors influence the overall security of an authentication system:
- Whether the authentication methods use independent factors.
- Whether verification can be intercepted or phished.
- How securely authentication credentials are stored.
- Whether account recovery procedures introduce weaknesses.
- Whether the service protects against suspicious login attempts.
For most users, enabling a strong additional authentication method is considerably better than relying on a password alone.
Different Types of Two-Factor Authentication Methods
Not every authentication method offers the same level of protection. Understanding the available options helps users choose a suitable method for their accounts.
SMS Verification Codes
SMS verification uses text messages to deliver one-time codes to a registered mobile number.
After entering a password, the user receives a code and enters it into the login page.
This method is relatively easy to use because most people already have access to a mobile phone. However, it has limitations.
Attackers may exploit SIM-swapping attacks to gain control of a victim’s phone number. SMS codes can also be captured through phishing attacks.
SMS verification is better than having no additional protection in many situations, but stronger alternatives are preferable when available.
Authenticator Applications
Authenticator applications generate temporary verification codes, commonly using the Time-based One-Time Password (TOTP) standard.
Instead of receiving a code through a mobile network, the application generates one locally using a shared secret and the current time.
The code changes periodically, usually every 30 seconds.
This approach avoids several risks associated with SMS delivery. However, it isn’t completely phishing-resistant. An attacker operating a convincing fake login page may capture a password and a currently valid authentication code.
Authenticator applications are a useful security improvement over SMS for many accounts, but users should still be careful about suspicious login pages.
Push Notifications
Push authentication sends an approval request to a registered device when someone attempts to sign in.
The user receives a notification and can approve or reject the request.
Some services use number matching, requiring users to enter or select a number displayed on the login screen. This helps reduce the risk of accidentally approving fraudulent requests.
However, repeated approval notifications can still be used in push-fatigue attacks. Users should never approve a login request they didn’t initiate.
Hardware Security Keys
Hardware security keys are physical devices used to authenticate a user through cryptographic verification.
Depending on the implementation, they can connect through USB, NFC, or another supported interface.
FIDO2 security keys use public-key cryptography and can provide phishing-resistant authentication through WebAuthn.
Unlike manually entered verification codes, the authentication process is bound to the legitimate website’s identity. This makes it substantially harder for an attacker to reuse authentication credentials on a fraudulent website.
For accounts that support them, hardware security keys are a strong option.
Passkeys
Passkeys are a newer authentication technology designed to make sign-ins both easier and more resistant to phishing.
They use public-key cryptography rather than relying on traditional passwords or manually entered one-time codes.
A passkey can be protected through a device PIN, fingerprint, or facial recognition, depending on the device and implementation.
When user verification is performed as required, passkeys can provide phishing-resistant multi-factor authentication.
They also allow passwordless sign-in, which means users may not need to enter a conventional password at all.
This makes passkeys an important development in account security rather than simply another type of verification code.
Can Hackers Bypass Two-Factor Authentication?
Yes. Two-factor authentication significantly improves account security, but it doesn’t make an account impossible to compromise.
Attackers use several techniques to get around authentication protections.
SIM swapping: An attacker attempts to transfer a victim’s phone number to another SIM card or device. If successful, the attacker may receive SMS verification codes intended for the victim.
Real-time phishing: Fraudulent websites imitate legitimate login pages. When a victim enters their password and verification code, the attacker attempts to use those details on the real service before the code expires.
Push fatigue: Attackers repeatedly send login approval requests, hoping that the account owner eventually approves one out of frustration or confusion.
Account recovery attacks: Weak recovery procedures can allow attackers to regain access without defeating the primary authentication method.
These risks demonstrate why choosing a strong authentication method matters. Phishing-resistant authentication, such as properly implemented FIDO2 credentials, can reduce exposure to several common credential-theft techniques.
Users should also protect their recovery email addresses, keep their devices updated, and avoid sharing authentication codes with anyone.
What Happens If You Lose Your Authentication Device?
Losing the phone or security key used for account verification can make signing in difficult, particularly when the device is the only available authentication method.
This is why recovery planning should happen before an emergency.
Depending on the service, recovery options may include:
- Backup codes: One-time codes generated in advance for situations where the primary authentication method is unavailable.
- A second registered device: An alternative trusted device that can complete authentication.
- Additional security keys: A backup physical key registered with the account.
- Account recovery: The service’s official process for verifying ownership and restoring access.
Users should store backup codes somewhere secure and separate from the device they protect.
It’s also important to remember that account recovery is part of the security system. A strong login method cannot provide complete protection if an attacker can easily bypass it through a poorly protected recovery process.
Which Authentication Method Should You Choose?
The right choice depends on the accounts you use, the security options available, and the consequences of losing access.
For most people, a sensible approach is to enable the strongest authentication method supported by each important service.
Consider these practical recommendations:
For everyday accounts: Use an authenticator application when stronger phishing-resistant options aren’t available. Enable additional verification rather than relying on a password alone.
For email and financial accounts: Prefer passkeys or hardware security keys where supported. These accounts deserve particular attention because they may provide access to other services or sensitive information.
For business accounts: Encourage phishing-resistant authentication, establish recovery procedures, and use appropriate account-management controls.
For accounts that only support SMS: Enable SMS verification rather than leaving the account protected by a password alone, while recognizing its limitations.
You should also maintain backup authentication methods and secure your recovery information.
The goal isn’t to collect as many verification steps as possible. It’s to use authentication methods that provide meaningful protection without creating unnecessary barriers to legitimate access.
Frequently Asked Questions
Is two-factor authentication the same as two-step verification?
Not necessarily. Two-factor authentication requires two different authentication factors, while two-step verification requires two verification steps. Some services use the terms interchangeably, but their technical meanings are different.
Is 2FA more secure than two-step verification?
Not automatically. Security depends on the authentication methods and how they are implemented. Properly configured phishing-resistant authentication generally offers stronger protection than methods relying on manually entered codes.
Can two-step verification use the same factor twice?
Yes. A system could require a password and PIN as separate verification steps. However, both belong to the knowledge category, so they don’t constitute two-factor authentication.
Is SMS verification considered 2FA?
SMS verification can be part of 2FA when it is combined with an independent authentication factor, such as a password. However, SMS has security weaknesses, including SIM swapping and phishing.
Is an authenticator app safer than SMS?
Generally, authenticator applications avoid some risks associated with SMS delivery and phone-number takeover. However, manually entered authenticator codes can still be captured through real-time phishing.
Are passkeys a form of two-factor authentication?
Passkeys can provide multi-factor authentication when the implementation requires user verification, such as a device PIN or biometric check. They also provide phishing-resistant authentication through cryptographic website verification.
Can hackers bypass two-factor authentication?
Yes. Attackers may use phishing, social engineering, compromised devices, or weaknesses in account recovery systems. Phishing-resistant authentication helps defend against important categories of attacks but cannot eliminate every security risk.
Should I enable two-step verification on every account?
Enable additional authentication on accounts that support it, particularly email, financial, cloud-storage, and social media accounts. Choose stronger methods when available and keep secure recovery options ready.
Final Thoughts
Two-factor authentication and two-step verification are closely related, but they describe different aspects of account security. One focuses on using different authentication factors, while the other describes completing two verification steps.
The distinction becomes more important as authentication technology evolves. SMS codes and authenticator applications remain common, but passkeys and hardware security keys offer stronger protection against phishing when correctly implemented.
Rather than focusing only on the terminology used by a website, examine how it verifies your identity and what happens if someone tries to access your account without permission.
A strong password is a useful starting point. Combining it with appropriate additional authentication, protecting recovery options, and choosing phishing-resistant methods wherever possible can make your online accounts considerably harder to compromise.